
Installation Guide for TeamConnect O365 Add-in 4.2
TeamConnect O365 Add-in 4.2 integrates TeamConnect with Outlook using Microsoft’s latest Add-in technology.
This guide covers prerequisites, system requirements, step-by-step installation, manifest generation, deployment, and troubleshooting.
Once deployed, the Add-in configuration is automatically available to end users within the timeframe specified by Microsoft.
Introduction
TeamConnect O365 Add-in 4.2 introduces a different way to integrate with Microsoft Outlook, leveraging the Microsoft Add-in technology. Its purpose is to empower attorneys and users by allowing them to conveniently access commonly used TeamConnect features through Outlook 365, rather than TeamConnect. To locate and determine the user’s TeamConnect version refer to the Upgrade Scenarios for TeamConnect O365 Add-in.
The TeamConnect O365 Add-in 4.2 is deployed to the end users using the admin center of the Microsoft 365 and needs to be handled by the client's IT irrespective of the fact whether they are a hosted TeamConnect client or deploy TC on-premise.
Setup and Access Requirements
Prerequisites for TeamConnect O365 Add-in 4.2:
Following are the prerequisites before you begin installing the TeamConnect O365 Add-in 4.2:
- Microsoft Account: A valid Microsoft O365 account is required.
- Supported Operating Systems: Compatible with desktop environments on both Windows and macOS.
- Supported Browsers:
- Google Chrome
- Microsoft Edge
- Mozilla Firefox
- Safari (version 17.2.1 or above)
- Installation of TeamConnect O365 4.x module via Available Updates in Admin Settings → About.
Compatibility
- TeamConnect Version Compatibility:
- The O365 Add-in 4.2 is compatible only with TeamConnect Enterprise version 7.2 or higher.
- Appointment Migration:
- Supported for TeamConnect 7.1 PB1 and above.
- Only applicable for users who were using appointments in the Outlook Plug-in.
- Task Migration:
- Supported for TeamConnect 7.2 and above.
- Only applicable for users who were using tasks in the Outlook Plug-in.
Add-in Limitations
- We do not support using the previous Office Suite Plug-in (for Outlook) and the new Add-in simultaneously. It is highly recommended to uninstall the previous Plug-in before proceeding with the installation of the new Add-in.
- File check-in/check-out is supported in the Outlook Add-in, rather than in Word, PowerPoint, and Excel. Users can efficiently manage files through Outlook Add-in or directly through TeamConnect for seamless file handling.
Outlook Integration with TeamConnect
Prior to initiating the integration process, it is advisable to examine the Admin guide accessible through the following link: Admin Guide
Azure Keys for Graph API Configuration
TeamConnect utilizes the Microsoft Graph API for communication with the Microsoft Exchange server. Below are comprehensive, step-by-step instructions on configuring Azure keys for Graph API.
| Instructions | Screenshot for Reference |
|---|---|
|
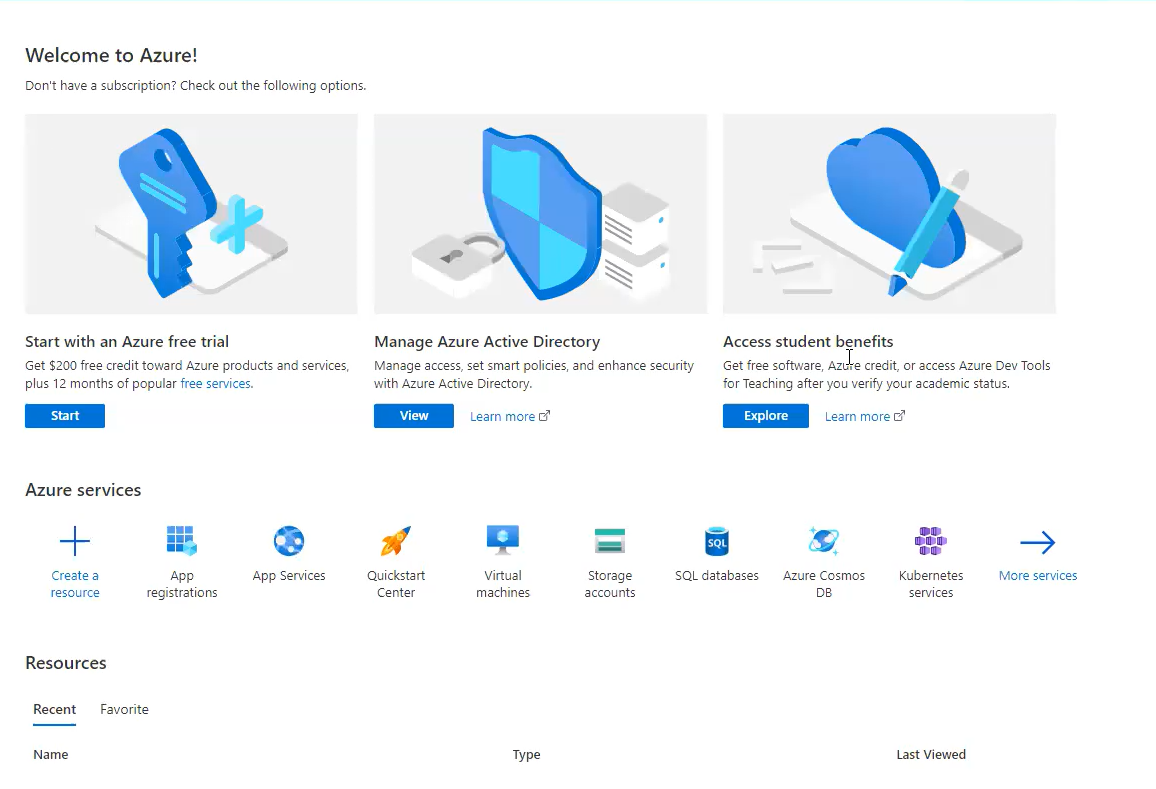
1. Go to the Azure Active Directory. (Note: This website is external and managed by Microsoft, not under the Mitratech domain.) 2. Sign in with your Azure admin account that has administrative privileges to the organization’s M365 domain.
|
 |
|
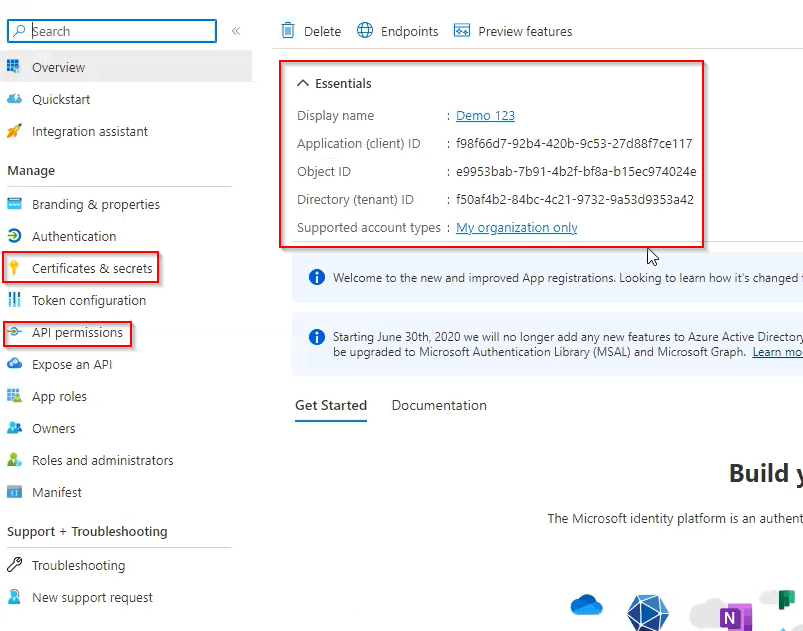
3. Click on App Registrations → New Registrations. 4. Enter a name for the registration. 5. Select the ‘Single Tenant’ option for Supported Account Types. 6. Click the Register button. |
 |
|
Step1: Configure Azure Keys for Graph API Delegated Permissions
|
 |
|
|
|
Step 2: Set Permission Type for Office Suite
|
 |
|
 |
|
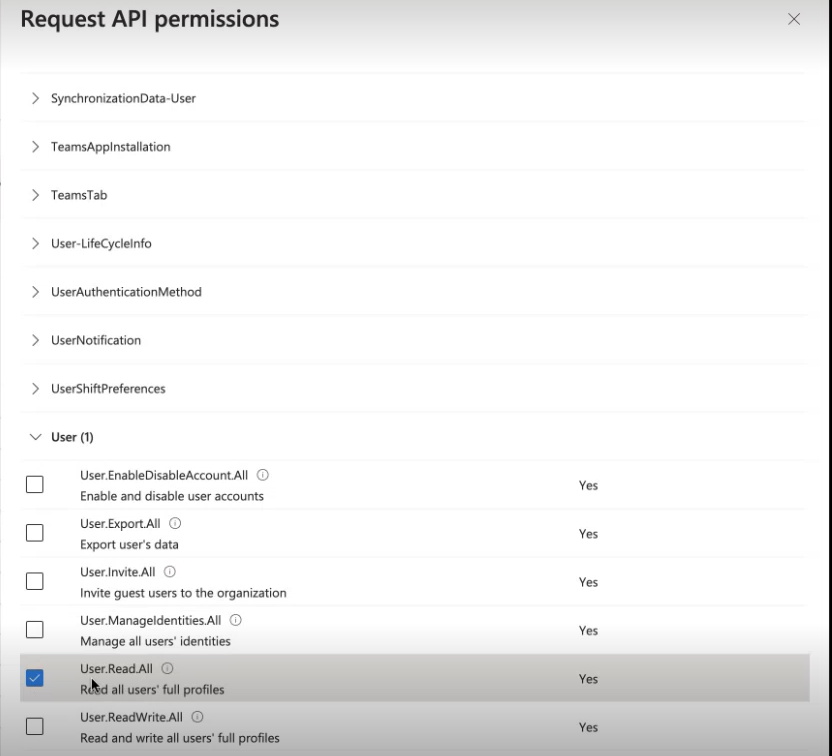
7. Go to the API Permissions tab on the left task pane. 8. Click Add a Permission. 9. Select Microsoft Graph → Application Permissions. 10. Click Add Permissions. 11. Search for User Permissions and add ‘User.Read.All’. 12. Search for Calendars and add 'Calendars.ReadWrite'. |
 |
|
14. The added permissions are displayed. You need to grant admin consent for all the permissions added. |
 |
|
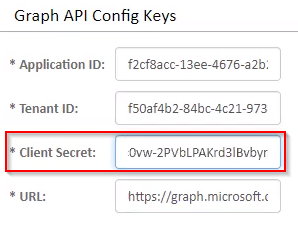
15. To grant permissions, go to the Certificates & Secrets tab on the left task pane → New Client Secret → Add a description. 16. Once the new client secret is added, copy the Client Secret Value as it will disappear if you navigate away from the page. 17. Paste the copied value at TeamConnect instance, navigate to Admin → Admin Settings → Office Suite → Graph API Config Keys → Client Secret. |
 |
| 18. Go back to Overview (Azure page)→ copy the Application (Client) ID, paste it at Graph API Config Keys (in TeamConnect) → Application ID. | 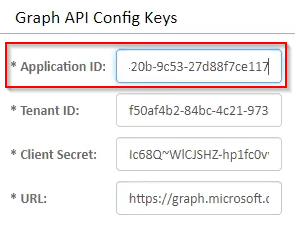 |
| 19. Go back to Overview (Azure page) → copy the Directory (Tenant) ID, paste it at Graph API Config Keys (in TeamConnect) → Tenant ID. | 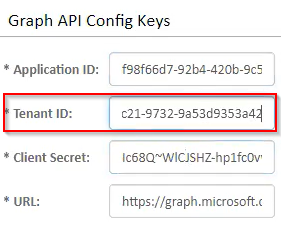 |
|
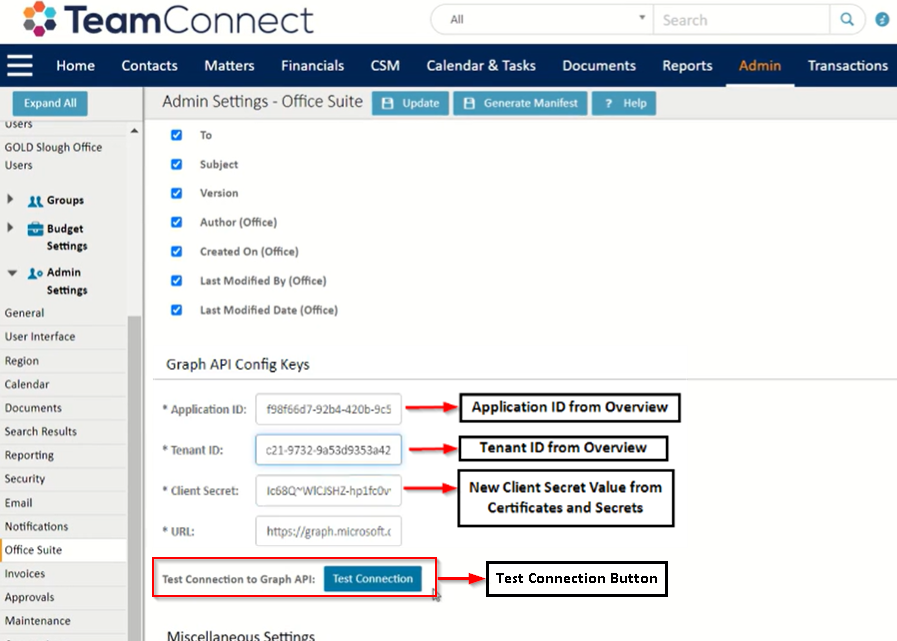
20. Click the Update button. The Azure Keys for Graph API are now configured. |
 |
Managing Permission Type Setting
-
Change Permission Type (anytime later, if required)
- Navigate to TeamConnect → Admin → Office Suite.
- In the Permission Type option, modify settings as needed:
- A radio button selection allows admin users to choose from:
- Delegated Permissions
- Application Permissions
- None

-
Default Behavior Based on Client Type:
- For Plug-in Clients:
- The default option is set to None to ensure no impact on existing configurations.
- For Add-in Clients:
- The default option is also set to None.
- Admins must manually select either Delegated Permissions or Application Permissions as required.
-
Mandatory Configuration for Admin Users:
Admins are required to populate all fields under the Graph API Keys section when selecting Application Permissions or Delegated Permissions. -
Migration Requirement:
During migration, admins must manually set the Permission Type for Application Permissions to ensure proper configuration. -
Reauthentication:
If a user has been inactive for an extended period or not logged in for a while, they are prompted to log in again.
Admin Options: If "Application Permissions" are selected, the process works as it does for versions TCE 7.2 and below.
Permissions Mentioned:
The following permissions apply to the Application Permissions.
- User.Read.All (to access basic user details and facilitate login)
- Calendars.ReadWrite (to manage calendars)
CAUTION: Do not use Tasks with Application Permissions.
The Tasks functionality is not supported when the Permission Type is set to Application Permissions. If Tasks is enabled with Application Permissions, both Tasks and Appointments stop working. To use Tasks, select Delegated Permissions in TeamConnect → Admin → Office Suite → Permission Type.
Revoking Consent for Delegated Permissions
Admins can revoke the consent granted by a user for delegated permissions during their login to the Outlook Add-in. To fully revoke their access, the tokens need to be invalidated through the Graph API. Refer to the following Microsoft documentation to revoke the consent manually.
Changing Permission Type in TeamConnect
When Delegated Permissions are enabled, access and refresh tokens are stored individually and stay saved. If you switch from Delegated Permissions to Application Permissions or None, these tokens remain stored but become unused. To remove them, an admin must manually clear previously stored access and refresh tokens from the TeamConnect database manually using SQL query. This step is optional.
However, Microsoft still considers these tokens valid, so they can remain in the TeamConnect database.
Test Connection Button
To verify the Graph API connection, the user can find a button to test the connection under Admin Settings → Office Suite, located below Graph API Config keys. In case the test connection fails, the error details will be recorded in the error logs. (Refer above image.)
How to generate the Manifest file?
A Manifest File is an XML document that describes the manifest, or package contents, of a Windows software application. It is pre-configured by Mitratech and hence any customization to this file is not supported. The manifest file is used to deploy the Add-in from the Microsoft Admin Center.
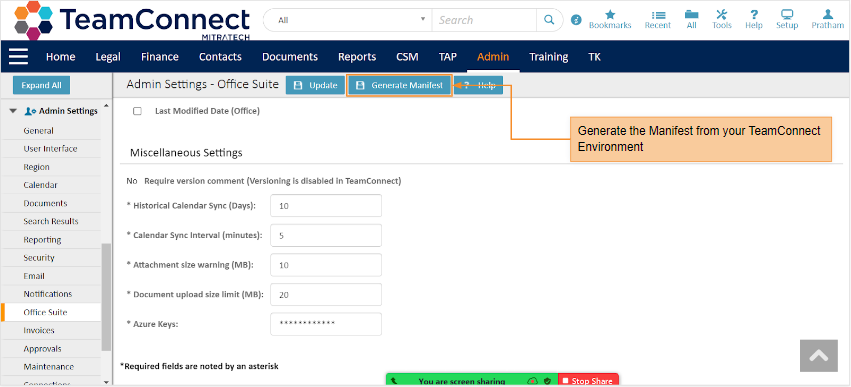
Each TeamConnect Environment will have its own manifest file. You can generate the manifest from your Teamconnect environment.
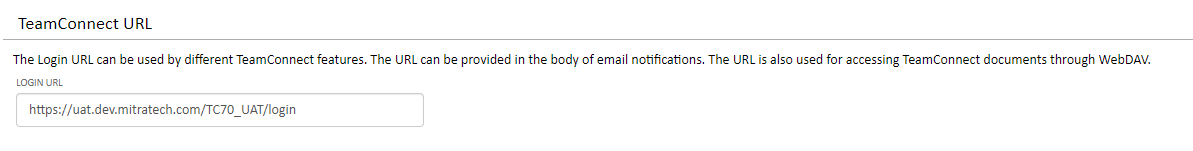
- Open TeamConnect and log in with your credentials.
- Click Admin → Admin Settings → Office Suite → Generate Manifest.
- The generated manifest will be saved in your local storage.
Note: Multiple manifest files can be generated and deployed.
Add-in Deployment
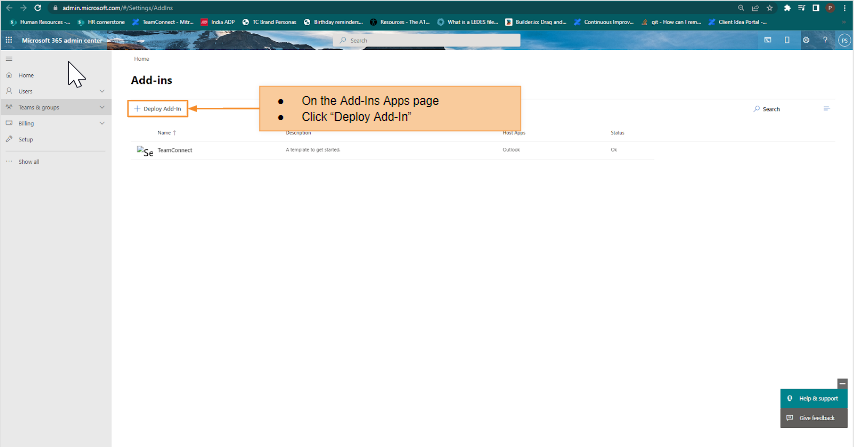
Once you get your manifest file, follow the steps below to deploy the Add-in. TeamConnect O365 Add-in 4.2 deployment requires Microsoft 365 and Exchange Online.
Follow the instructions below to deploy the Add-in from the Microsoft Admin Center:
| Instructions | Screenshot for Reference |
|---|---|
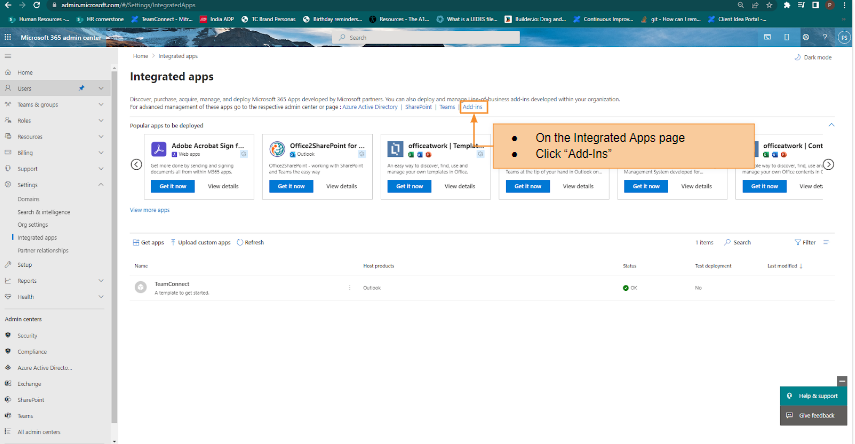
| 1. Navigate to your Microsoft 365 Admin Center or admin.microsoft.com and search for Add-ins in the search bar or go to Settings → Integrated Apps. | 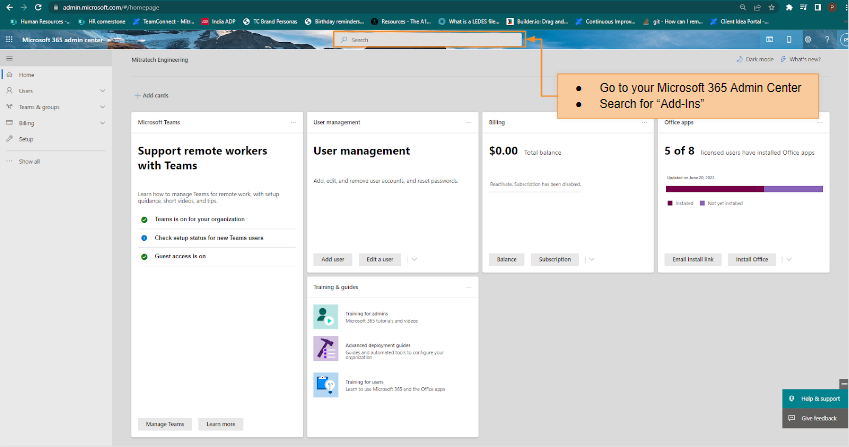 |
|
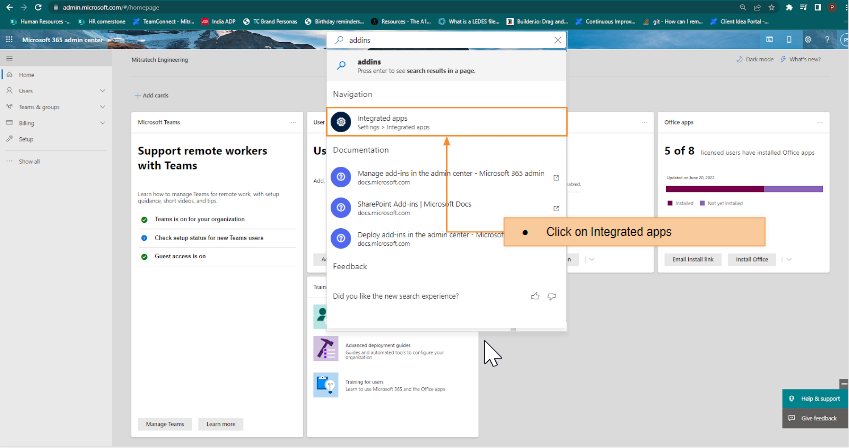
2. In the search results, from the options displayed, click Integrated apps. |
 |
| 3. The Add-in can be deployed in two different ways: | |
|
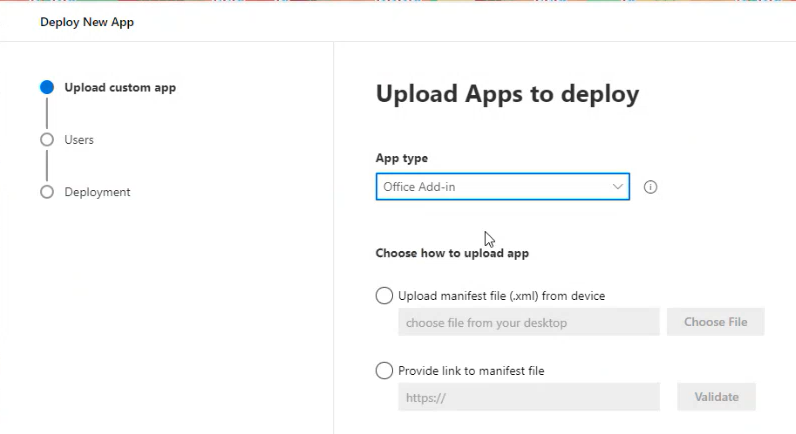
4. Method 1: (Recommended) a. Select Add-ins on the Integrated Apps page. |
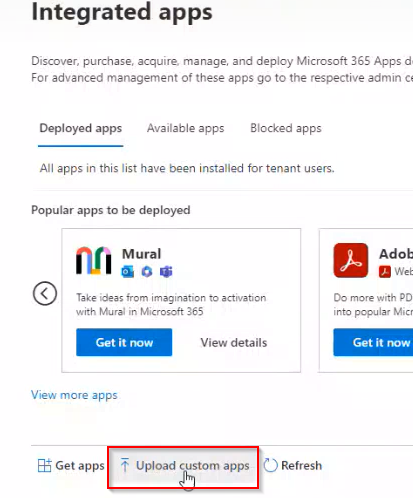
4. Method 2: a. Click Upload custom apps on the Integrated apps page. |
|
b. Click the Deploy Add-in button. |
b. Deploy New App modal is displayed. Select Office Add-in from the App Type drop-down options. |
|
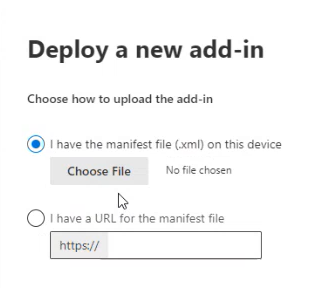
c. Deploy a new Add-in modal is displayed. Click the Upload Custom Apps button. 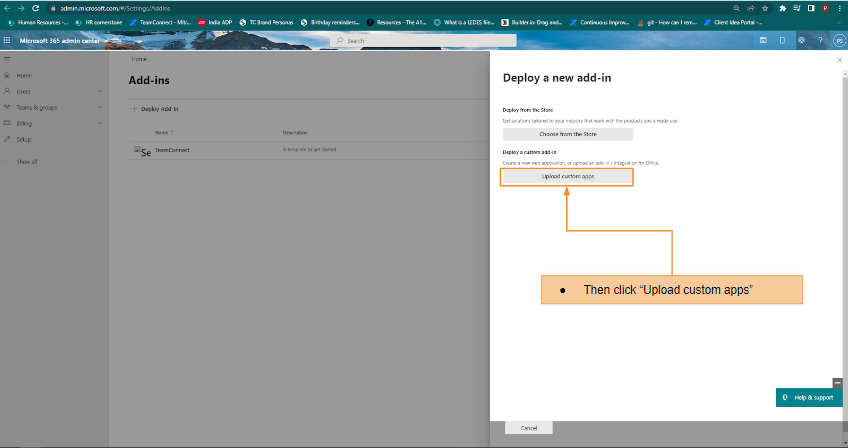 |
c. Select the Upload manifest file from the device and choose the manifest file provided to you by Mitratech and click the Next button. |
|
Select I have the manifest file option and click Choose File. Upload the manifest file generated through the Microsoft Admin Center and click the Upload button. |
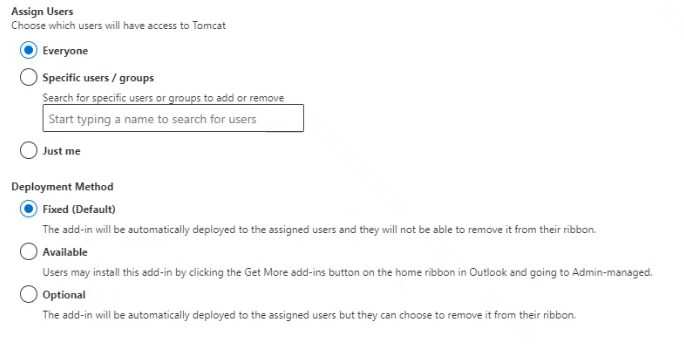
Select the availability of the Add-in to the users by selecting the Assign Users radio button. |
|
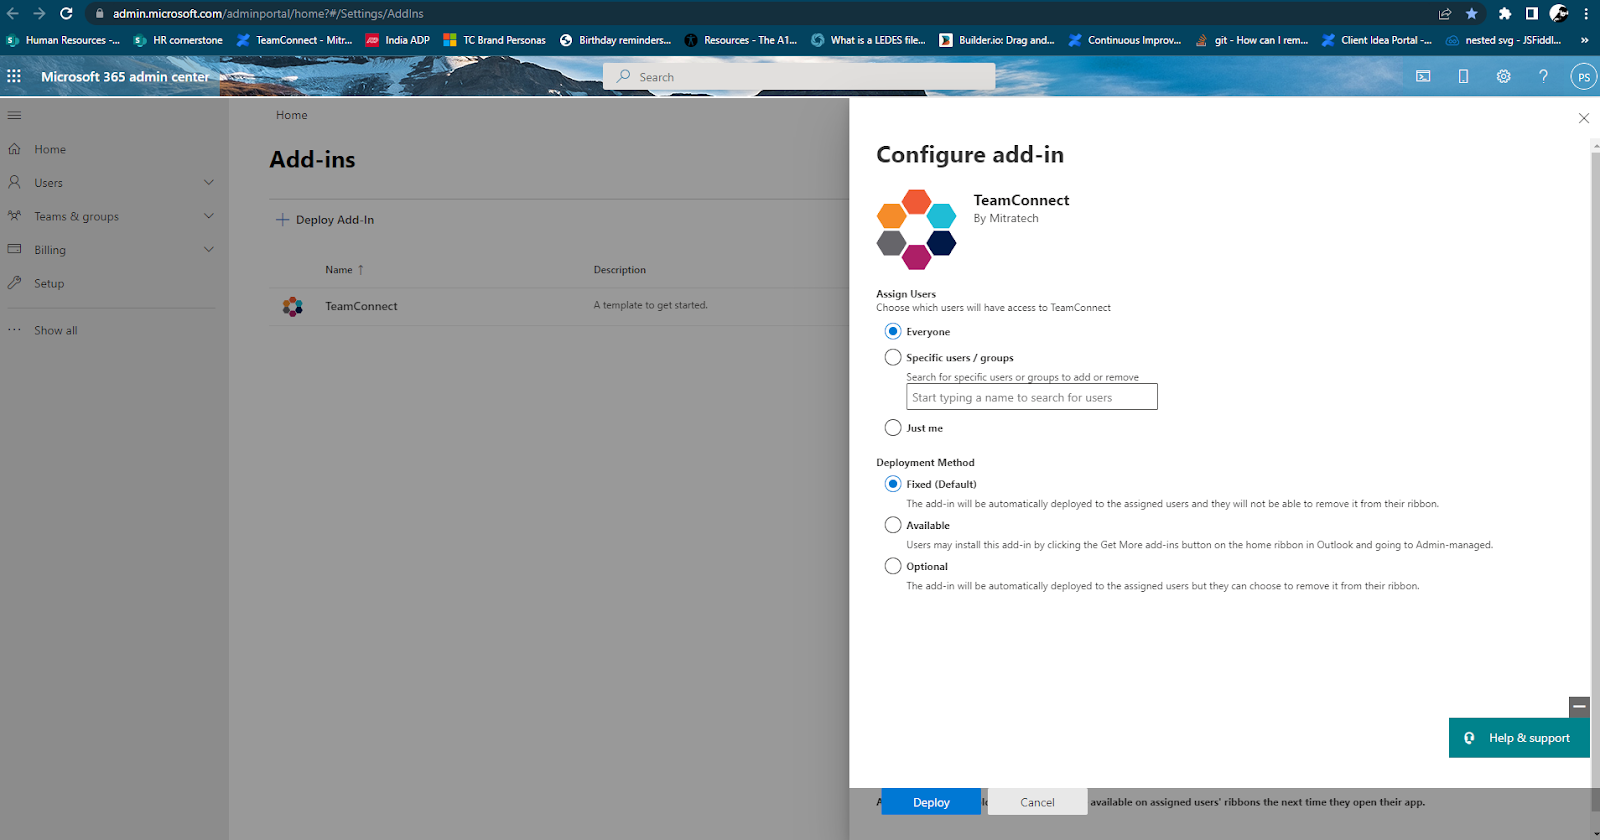
d. The Configure Add-in modal is displayed. Configure the settings as per your organization. |
d. Click the Next button.
|
|
e. Finally, click the Deploy button. |
e. Click the Deploy button. Note: Configuration options are not available in this method. |
|
5. The Add-in will be deployed and it will be automatically available within the duration mentioned by Microsoft post-deployment. Note: This website is external and managed by Microsoft, not under the Mitratech domain.
5. The TeamConnect icon is present in every Outlook mail of the end user. Clicking the icon |
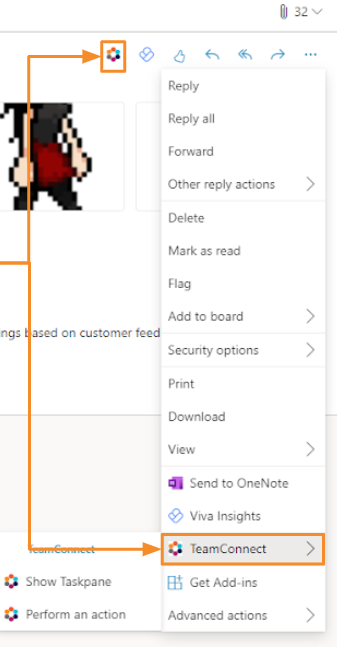 |
 will display the TeamConnect task pane on the screen.
The latest TeamConnect Outlook 365 Add-in can be updated through the Microsoft 365 Admin Center, utilizing the updated Manifest file from your TeamConnect Instance (provided the Manifest File has been updated).
There are certain functions in the admin interface that only the organization administrators can perform to set limitations or ease of use for the end users. For a detailed list of tasks achievable by administrators, refer to the following document: Admin Guide
Frequently Asked Questions
FAQs
How Can Users Revoke Accepted Permissions?
Currently, users cannot manage or revoke permissions directly within TeamConnect or the Add-in. All permission management must be handled through Microsoft Graph API.
Why Use Delegated Permissions?
Application-level permissions use a single token shared across all users, which poses a security risk. If this token is compromised, it grants access to all users' data. In contrast, delegated permissions issue separate tokens for each user, ensuring individualized access and enhanced security.